Ad
Blog
A collection of useful articles for developers and software enthusiasts. Learn about the latest trends and technologies in the community.
Effective TFA policy is the Important line in Directus 12.5
Directus v12.5.0 is flagged Important as a breaking change. The partner-break line is two-factor enforcement now resolving from effective policies (#28176) plus stricter ip_access validation, not the Preview Base URL setting.
•3 min read
Login redirect creds is the Important line in pnpm 12.9
pnpm 12.9 is flagged Important as a security fix. The partner-break line is pnpm login forwarding credentials in the request body to another origin during redirects, not WebAssembly in StackBlitz.
•2 min read
Supergraph JWT reuse is the Important line in Tyk 5.15.1
Tyk Gateway v5.15.1 is flagged Important as a security fix. The partner-break line is federated GraphQL supergraph reusing the first caller's JWT across users (TT-17921), not the dependency CVE bump list.
•3 min read
Cert parsing DoS is the Important line in Envoy 1.39.2
Envoy Proxy v1.39.2 is flagged Important as a security fix. The partner-break line is CVE-2026-35189 (TLS cert parsing DoS via nameRelativeToCRLIssuer CRL DPs), not the Debian bullseye packaging removal.
•3 min read
CIBA token redemption is the Important line in Keycloak 26.7.5
Keycloak 26.7.5 is flagged Important as a security fix. The partner-break line is CIBA token redemption still issuing tokens for brute-force-locked accounts after an incomplete prior fix, not the long CVE list.
•2 min read
Direct-upload replay is the Important line in OpenProject 17.8.1
OpenProject 17.8.1 is flagged Important as a security fix. The partner-break line is reusable S3 direct-upload forms rewriting attachments after antivirus passed, not the bug-fix list.
•2 min read
Routes redaction is the Important line in Skipper 0.28.19
Skipper v0.28.19 is flagged Important as a security fix. The partner-break line is supportListener /routes redacting inline secrets (default :9911), not the multiarch Docker image note.
•2 min read
Public proxy trust is the Important line in Echo 4.16 and 5.4
Echo v4.16.0 and v5.4.0 are flagged Important as breaking changes. The partner-break line is Context.Scheme() ignoring X-Forwarded-Proto from public CDN and LB peers (HTTPSRedirect loops, HSTS stops), not the upgrading-is-recommended opener.
•2 min read
Removed gradient agent is the Important line in doctl 1.175.0
doctl v1.175.0 is flagged Important as a breaking change. The partner-break line is removed doctl gradient agent (scripts fail), not the knowledge-base rename.
•2 min read
Host overwrite is the Important line in Podman 6.1.2
Podman v6.1.2 is flagged Important as a security fix. The partner-break line is CVE-2025-11395 on podman load and podman volume import overwriting host files, not the dependency bumps.
•2 min read
Removed v1 HTTP is the Important line in Jaeger 2.21.0
Jaeger v2.21.0 is flagged Important as a breaking change. The partner-break line is removed v1 HTTP endpoints (and ai.enable_mcp becoming optional ai.mcp), not ClickHouse going stable.
•2 min read
Header types is the Important line in Axios 0.34.0
Axios v0.34.0 is flagged Important as a breaking change. The partner-break line is TypeScript rejecting Promise, function, or custom toString headers (and NO_PROXY CIDR finally bypassing), not the caller diagnostics.
•2 min read
ClearBootstrap is the Important line in PocketBase 0.40.4
PocketBase v0.40.4 is flagged Important as a deprecation. The partner-break line is app.ResetBootstrapState() soft-deprecated for app.ClearBootstrap(), not the migration deadlock fix.
•2 min read
selfupgrade is the Important line in Grav, not 2.1.2
Grav put Important flags on 2.0.27, 2.1.1, and 2.1.2 the same day. The partner-break line is bin/gpm selfupgrade finally letting 2.0 sites climb to 2.1, not the newest patch tag.
•2 min read
mesh:write is the Important line in Consul 2.0.4
Consul v2.0.4 ships a BREAKING CHANGE on ACL permissions for Envoy extensions. The Important line is mesh:write (and the FIPS rename), not the patch tag.
•2 min read
230 security fixes is the Important line, not Stable Channel Update
Chrome 153 hit stable with 230 security fixes, including a CVE Google says has an exploit in the wild. The Important line is the patch count, not the channel title.
•2 min read
Check your metric names is the Important line in Telegraf 1.40
Telegraf v1.40.0 ships Important Changes for Cisco telemetry aliases and a power_on_hours unit flip. The partner-break line is the dashboards, not the new plugins.
•2 min read
October 2 is the Copilot deprecation line, not the new model
GitHub is retiring selected Copilot models on October 2, 2026. The line that matters is the date and the admin policy, not Gemini 3.8 Flash showing up.
•2 min read
Most users need no action is the Important line you skip
Heroku updated stacks 22, 24, and 26 with security fixes. The Important line is the container rebuild, not the calm opener.
•2 min read
Generally available is the migration line you can promise
GitHub marked Enterprise Live Migrations from GHES to ghe.com generally available. The Important line is the status word, not the CLI name.
•2 min read
Now stable is the CI line you can promise
Buildkite Agent v4 is now stable. The Important line is the upgrade guide, not systemd watchdog.
•2 min read
The HTTP client major is the break your AE never sees
Got v16.0.0 rewrote HTTP/2 and dropped proxy support. That is the Important line, not a library bump.
•2 min read
Last night's security cluster is the patch list
Gitea v1.27.3 and a Moleculer TCP DoS are the Important lines. Wekan version spam is not.
•1 min read
The Important flag is the partner-break line, not a badge
Shopify Theme CLI and script-tag deprecations are the Important lines. Recency is the shiny stuff.
•1 min read
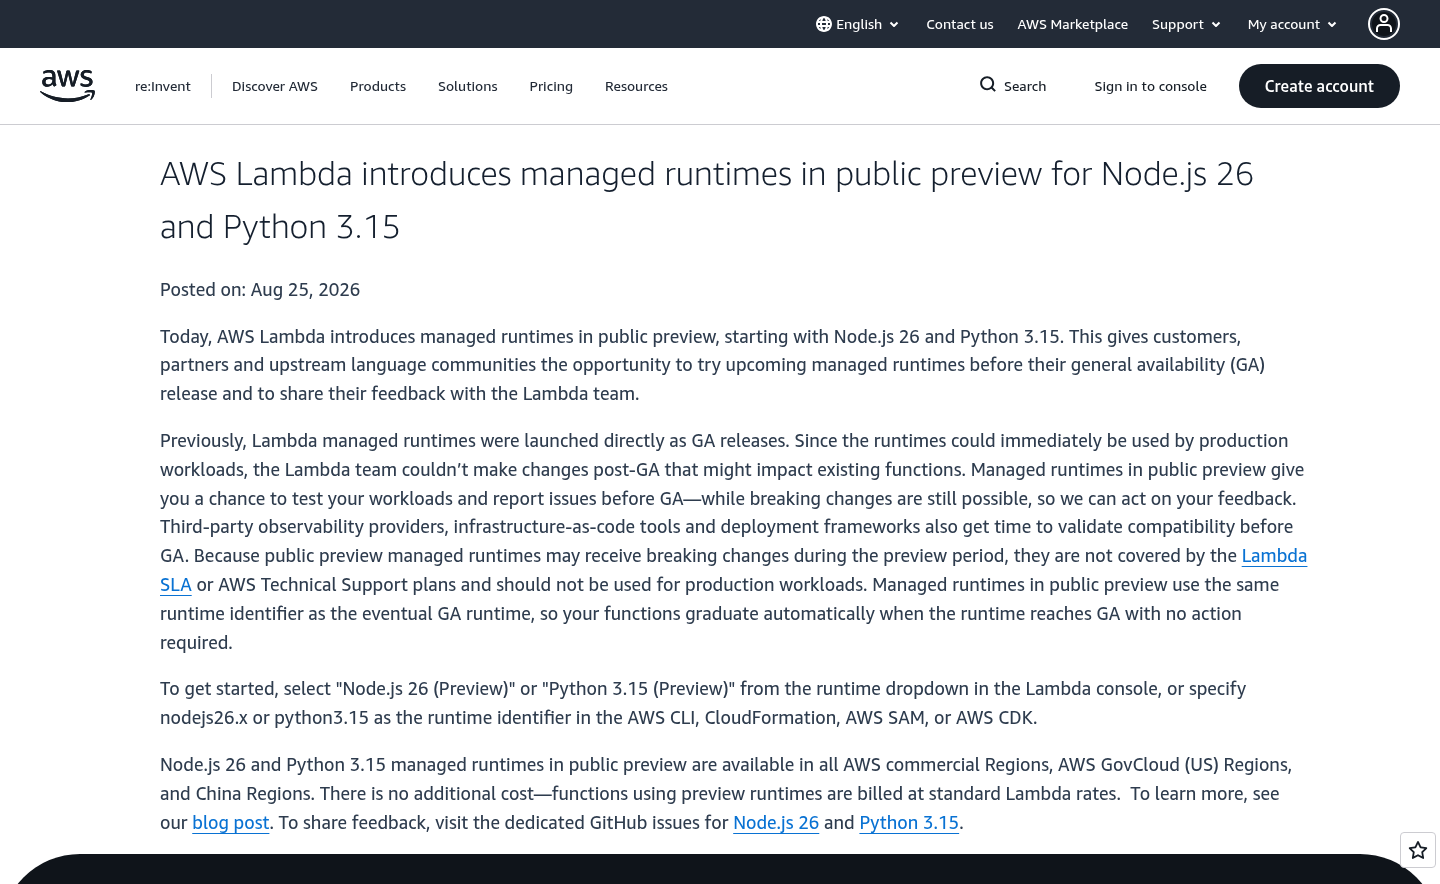
Public preview is the changelog line your AE misses
So AWS What's New on August 25: AWS Lambda introduces managed runtimes in public preview for Node.js 26 and Python 3.15. That's the kind of sentence that looks like a footnote until a prospect asks if you're on 26 yet and nobody on the call has seen the post.
•3 min read
Why GTM Teams Care About Changelog APIs
How uniform changelog data powers competitive intelligence, sales enablement, and marketing automation.
•2 min read
Understanding lastUpdatedAt: Company Time vs. Fetch Time
Why Watch Changelog tracks vendor published timestamps separately from our fetch times.
•2 min read
Introducing Watch Changelog: Uniform API for Vendor Changelogs
Stop writing custom scrapers. Watch Changelog aggregates hundreds of vendor changelogs into one uniform JSON API.
•1 min read